01
The idea
Firewall logs contain many individual technical events. FireWall turns them into structured, filterable and time-based security information.
SYSTEMS & INFRASTRUCTURE
See what reaches the network. Understand what gets blocked.
FireWall centrally evaluates firewall and VPN events. Live events, blocked inbound connections, attack sources, target ports, GeoIP data and VPN sessions are prepared in specialized monitoring views.
01
Firewall logs contain many individual technical events. FireWall turns them into structured, filterable and time-based security information.
02
Blocked connections, protocols, target ports, external sources, internal targets and VPN events occur continuously and are difficult to understand without preparation.
03
FireWall consolidates stored events into dedicated views for live monitoring, attack analysis, GeoIP evaluation and VPN visibility.
REAL CAPABILITIES
The public page only describes functionality present in the supplied FireWall files.
Total logs, block events, inbound and outbound blocks, unique sources, target ports and recent events.
Automatically refreshed events with metrics for the last minute, last hour, active sources and top port.
Evaluation of external inbound block events by sources, ports, targets, interfaces, protocols and time periods.
GeoIP aggregation of external block events by countries and cities plus map visualization.
Evaluation of active connections, logins, connection duration, sessions and VPN events.
LIVE EVENT INTELLIGENCE
The live area supports filtering stored firewall events by multiple technical criteria.
ATTACK INTELLIGENCE
The Attack Center focuses on external inbound blocked events and evaluates sources, target ports, targets, interfaces, protocols and time periods.
GEO INTELLIGENCE
GeoIP data can associate external sources with countries and cities and visualize aggregated events on a world map. The public ITpassion page does not publish real IP addresses or actual event data.
VPN VISIBILITY
The VPN area processes connect, IP assignment and disconnect events and derives session and usage information.
SHOWCASE VIEW
The neutralized showcase visual communicates the breadth of FireWall analysis without exposing operational data.
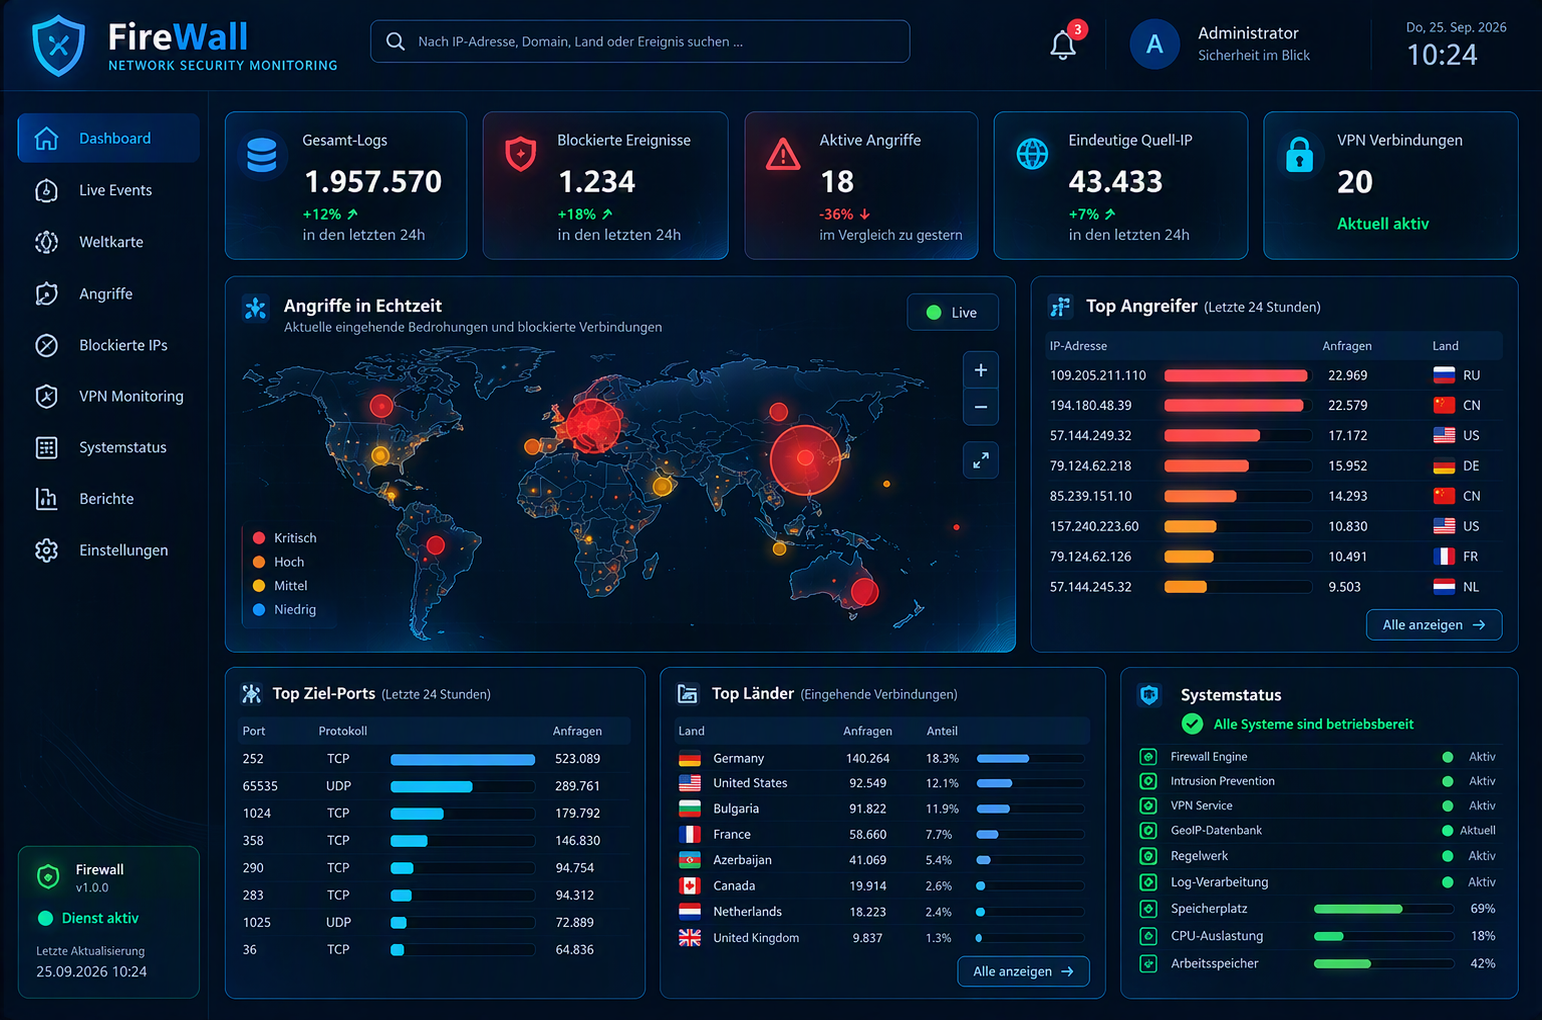
No internal addresses, host names, user identifiers or actual attack data are published on ITpassion.
PUBLIC SHOWCASE
The public presentation abstracts network ranges, systems, users, file paths and concrete internal integrations. Only functional concepts and neutralized product visuals are shown.